About
A security firm at its core.
Web Lock Smith Inc. exists for one reason. The people who run small and mid-sized businesses online have no security team, and the attackers hunting them never sleep. We stand in that gap.
What that means in practice
Most agencies build websites and treat security as a checkbox at the end. We start from the other end. Every engagement begins with the question an attacker asks: where is this site exposed, and how fast can it be closed? Then we fix the cause, not the symptom, and we prove the fix with a retest you can read.
- We work on the whole stack. PHP and WordPress, Node.js and Next.js, nginx and Apache, the Linux and AWS servers underneath, and the certificates and headers in front.
- We tell you the truth about what we saw. Our free check reports public observations and says plainly what it could not verify. No fake all-clears, and no invented findings.
- We never ask for passwords by email. If access is needed, we agree a method and the minimum permissions first.
- We agree the scope and the fee before any paid work. If we accept the work and cannot deliver the agreed fix, you get the service fee back.
From the founder
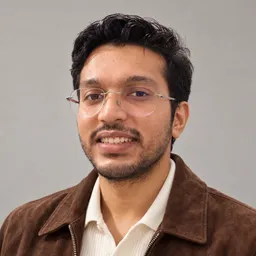
I started Web Lock Smith in the last week of October 2026, the week two critical PHP flaws were disclosed and exploit attempts passed into the millions within two days. I watched business owners refresh a homepage that looked completely normal and take that as proof they were safe. It isn’t proof of anything. The attacks that end businesses never change what the homepage looks like.
What struck me wasn’t the technology. It was how alone those owners were. Big companies have a security team and a playbook. A florist with an online shop, a clinic with a booking page, a two-person agency with twelve client sites: they have a hosting bill and a hope. I built this company to be the team they never had.
Our promise is simple. We will find the exposure, fix the cause, prove it is closed, and put it in writing you can show anyone. If we take your job and can’t deliver what we agreed, you don’t pay. I would rather lose a sale than tell you something is secure when I can’t prove it.
How we work
- Look before touching. We start with what the public internet can see, then with the access you choose to give us. Nothing is changed until we understand the cause.
- Agree the scope and the fee. You get a written scope, a success criterion, and a quote. Paid work starts when you approve it, never before.
- Fix the cause. Patching a runtime, closing a flaw, removing a backdoor, repairing what an upgrade breaks: whatever the agreed scope requires, done by hand.
- Prove it. We retest the known exploit paths against your site and record the result, including anything that could not be verified.
- Hand over in writing. A plain-language report of what was vulnerable, what changed, what was verified, and what to watch next. It is yours to keep or show your clients.
We cap paid work at 20 sites per week so that every one of them gets that attention.
Company details
- Legal name
- Web Lock Smith Inc.
- Trading as
- WebLockSmith
- Founder and CEO
- Rishabh Chulet
- hi@weblocksmith.com
- Website
- www.weblocksmith.com
- Payments
- Card payments through Stripe, after the scope and fee are agreed
Find out where you stand.
Run the free check, then claim one of this week’s 20 slots before they’re gone.
Scan my website